Knowledge / Analysis · #TEKLink212
TEKLink212: VMDK corruption does not establish ransomware
Knowledge brief from a VM power-loss case: distinguish DISKLIB observations, snapshot consistency and evidence required before attributing encryption.
 Enlarge ↗
Read the full technical article at TUNGTEK ↗
Contents
1. Evidence supplied#
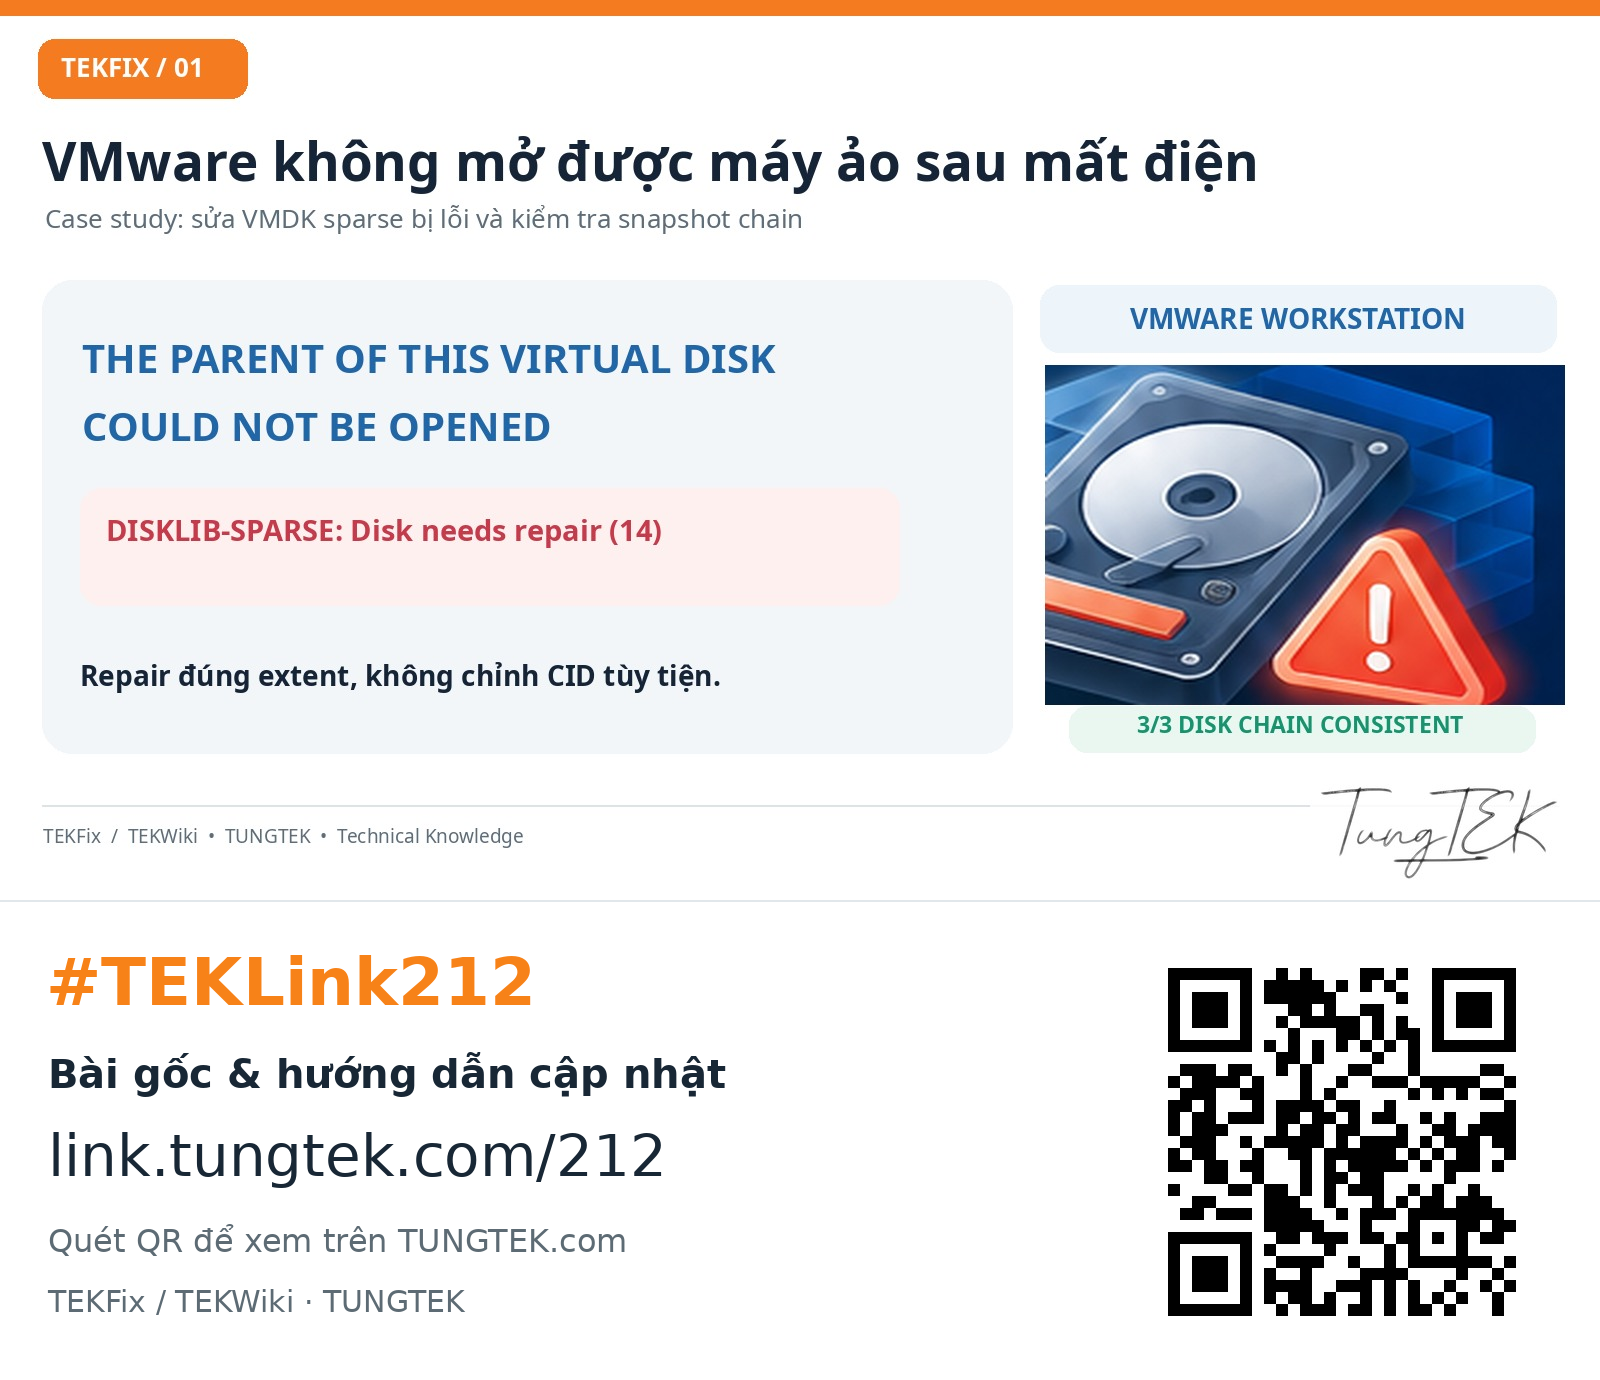
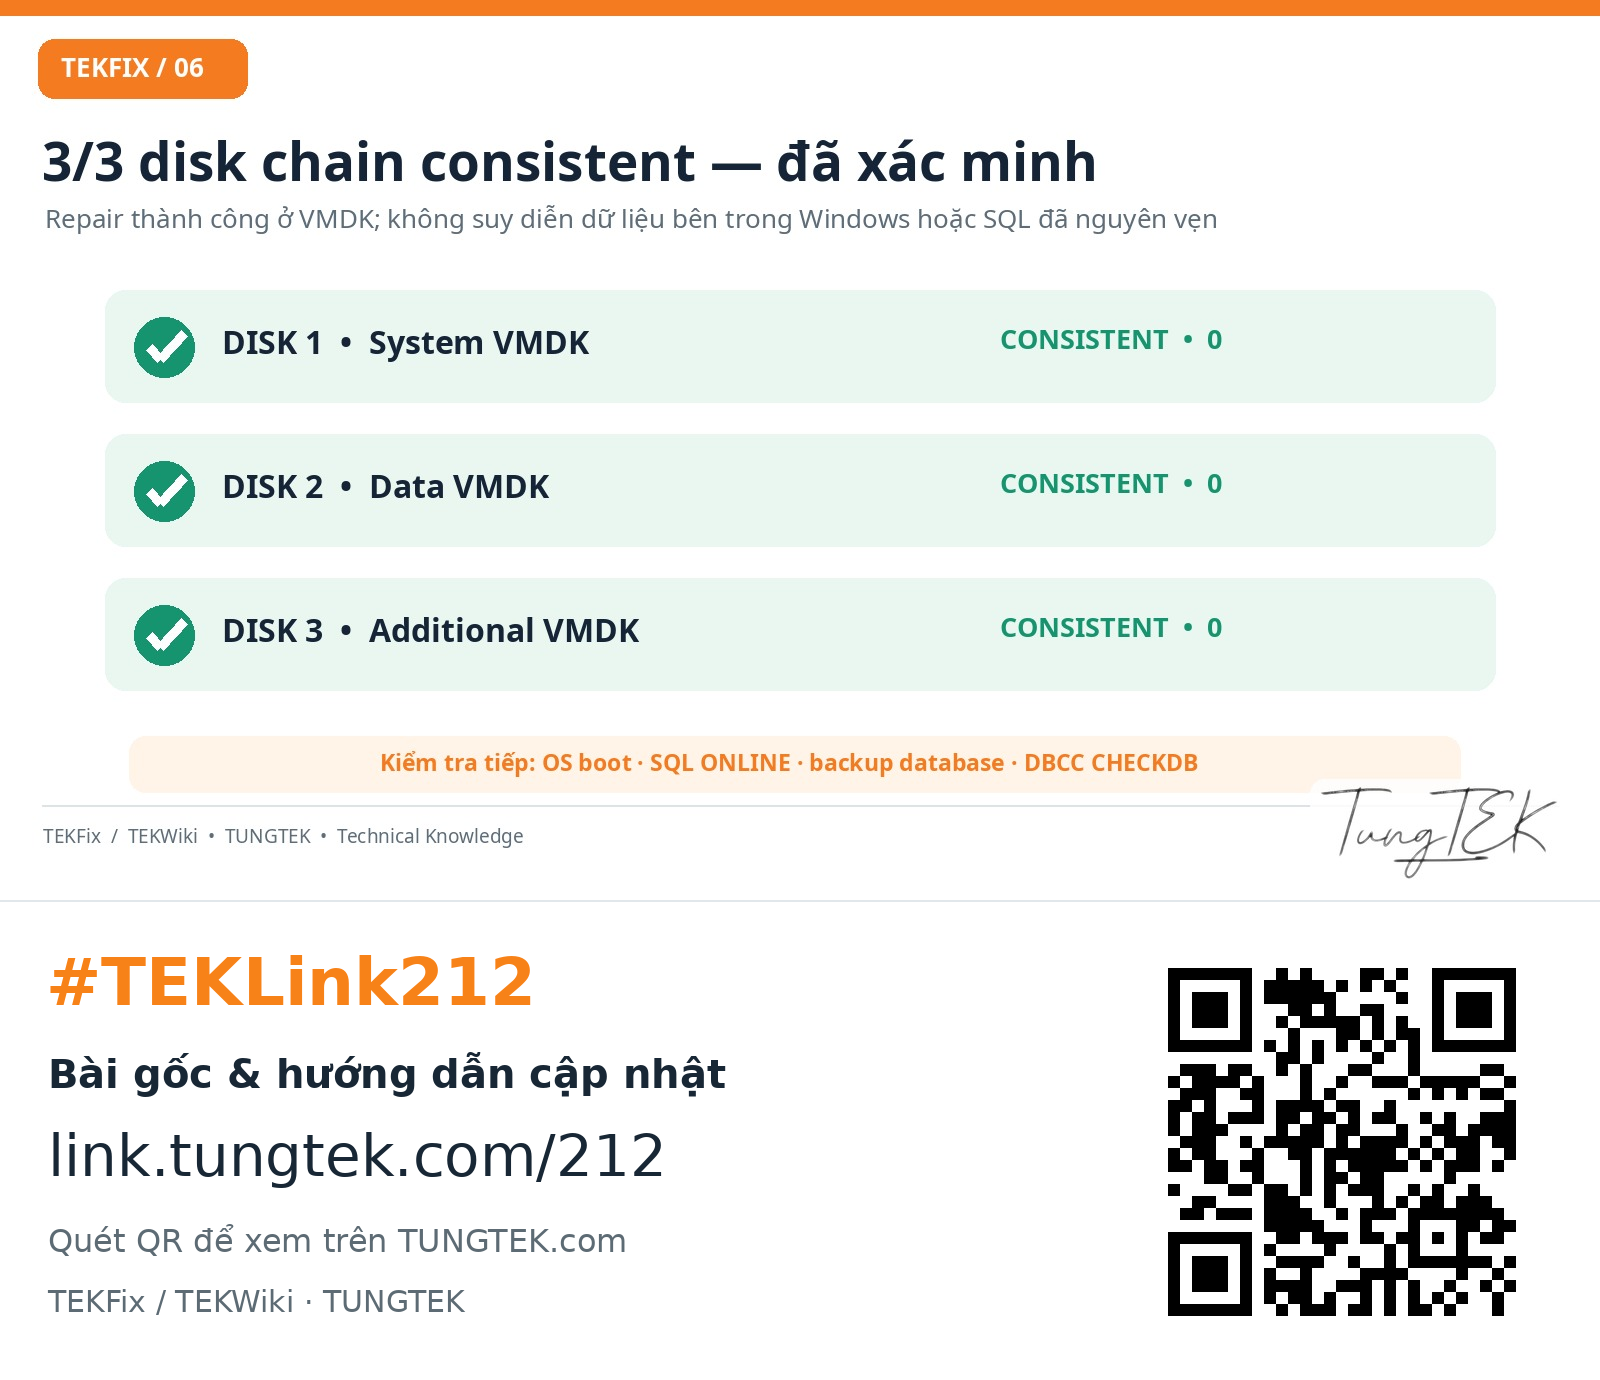
The anonymised TUNGTEK record describes a snapshot extent reporting Disk needs repair (14), a successful repair of the correct descriptor and three consistent VMDK chains with exit code 0. The record does not confirm Windows, SQL or application operation.
 Enlarge ↗
2. Respect the inference boundary#
Corruption describes a structural or data problem; encryption describes a cryptographic transformation. They can coexist, but a parent-open error or Disk needs repair does not establish ransomware. This case is not attributed to a ransomware family.
| Evidence group | Status in the public case description |
|---|---|
| DISKLIB / chain | Sanitised description available. |
| -R and -e results | Successful repair; three consistent chains; exit code 0. |
| Malware sample / ransom note / encryption behaviour | Not supplied for this case. |
| Boot / SQL / business validation | Unconfirmed. |
3. Further verification#
- Preserve the source and timeline, including operations before and after power loss.
- Where encryption is suspected, collect authorised artifacts rather than attributing from an extension.
- Validate application data after virtual-disk checks.
This is a knowledge brief, not an alert about a new ransomware campaign. Read the original TEKFix article for the investigation process and sample commands.
🇻🇳 Data incident? Call TUNGTEK.
Advice based on the actual state; preserve the original and agree scope before processing.
0963 509 115Source and limits
TUNGTEK — TEKFix / TEKWiki · #TEKLink212
Based on the anonymised TUNGTEK case record; no independent system validation. This case is not attributed to ransomware.