IDCF Cloud confirms ransomware: a lesson in backups outside the primary infrastructure
Three IDC Frontier notices from 7–9 October 2026 establish the cloud disruption, the disclosed scope and open recovery questions.
Ransomware.VNVerifiedRecently published content. Editorial dates and event dates are clearly distinguished.
Three IDC Frontier notices from 7–9 October 2026 establish the cloud disruption, the disclosed scope and open recovery questions.
Ransomware.VNVerified
A public warning and N-able's notice raise questions about centralized administration. Reference analysis, not a report of a new attack.
Ransomware.VNVerified
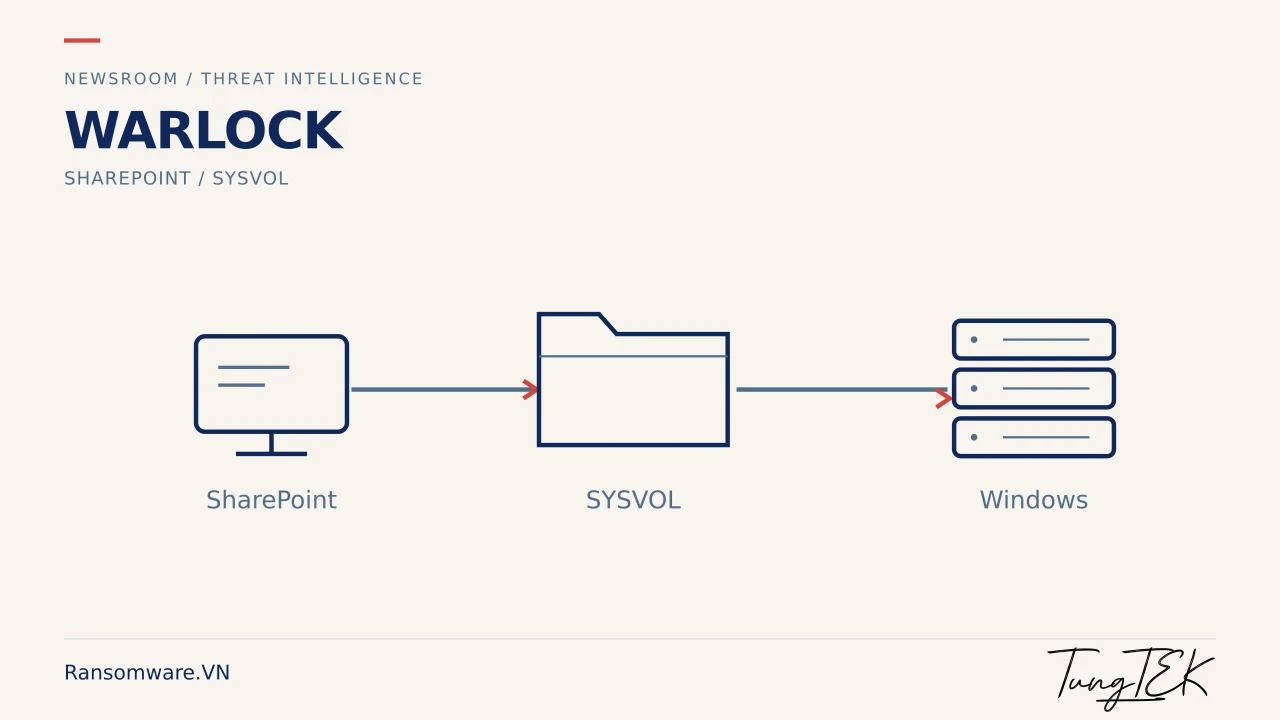
Symantec and Carbon Black's 1 October report highlights SharePoint entry and SYSVOL deployment. A focused reading for enterprise defenders.
Ransomware.VNVerified
No Ransomware knowledge for SMEs: encryption, data theft, decryptors, RAID and backups. Read indicators in context and avoid evidence-destroying reactions.
No.Ransomware.VNGuidance document
No Ransomware checklist: control connections, preserve evidence, assess backups and RFC for SQL, NAS, RAID, ESXi and Hyper-V before recovery.
No.Ransomware.VNGuidance document
Read TUNGTEK's public NAS record through its evidence: received devices, attribution limits and missing data.
Tùng TEKNot independently verified
Extensions and ransom notes are leads. Attribution requires comparable samples, behavior and timelines, with an explained confidence level.
Tùng TEKVerified
Understand each part of 3-2-1-1-0 and test whether backups are usable when the primary system fails.
Tùng TEKVerified
Combine logs, metadata and storage artifacts into a sourced timeline while retaining gaps and clock discrepancies.
Tùng TEKVerified
AA24-109A is a starting point for technical comparison, not evidence that an individual system is infected with Akira.
Tùng TEKVerified
Reference analysis of Microsoft's 2024 research, with questions for reviewing access and protecting virtualization infrastructure.
Tùng TEKVerified
Preserves the original Cyble, downtime, partial-encryption and RFC analysis while distinguishing claim publication from intrusion/encryption dates.
No.Ransomware.VNNot independently verified
Correcting attribution in the archive: separate CyRadar's MSSQL report from .PIZ, AnyDesk and Safe Mode hypotheses; retain log checklists and technical material for comparison.
No.Ransomware.VNNot independently verified
Eight internal tickets: ransom demands, indicators, reference TTPs and attribution limits. The .PIZ extension does not establish a family.
No.Ransomware.VNNot independently verifiedAlerts directly relevant to organizations, infrastructure and users in Vietnam.
Browse Vietnam coverageGlobal trends, new campaigns and lessons applicable to domestic systems.
Correlate information with IOCs, threat intelligence and preventive controls.
Threat IntelligenceIOC