IDCF Cloud confirms ransomware: a lesson in backups outside the primary infrastructure
Three IDC Frontier notices from 7–9 October 2026 establish the cloud disruption, the disclosed scope and open recovery questions.
Ransomware.VNVerifiedRansomware.VN covers news, alerts, threat intelligence, technical analysis and data from real cases.
Sources checked for the initial edition. Vietnam coverage is reference analysis, not a new incident disclosure. Verification methodology →

A public warning and N-able's notice raise questions about centralized administration. Reference analysis, not a report of a new attack.
Ransomware.VNVerified
Read TUNGTEK's public NAS record through its evidence: received devices, attribution limits and missing data.
Tùng TEKNot independently verified
Extensions and ransom notes are leads. Attribution requires comparable samples, behavior and timelines, with an explained confidence level.
Tùng TEKVerified
Understand each part of 3-2-1-1-0 and test whether backups are usable when the primary system fails.
Tùng TEKVerifiedRansomware.VN Threat Map tracks ransomware victim claims, groups and country-level activity trends using public threat intelligence sources.
Preparing Threat Map…
Read claims alongside their sources and verification statuses.
Three IDC Frontier notices from 7–9 October 2026 establish the cloud disruption, the disclosed scope and open recovery questions.
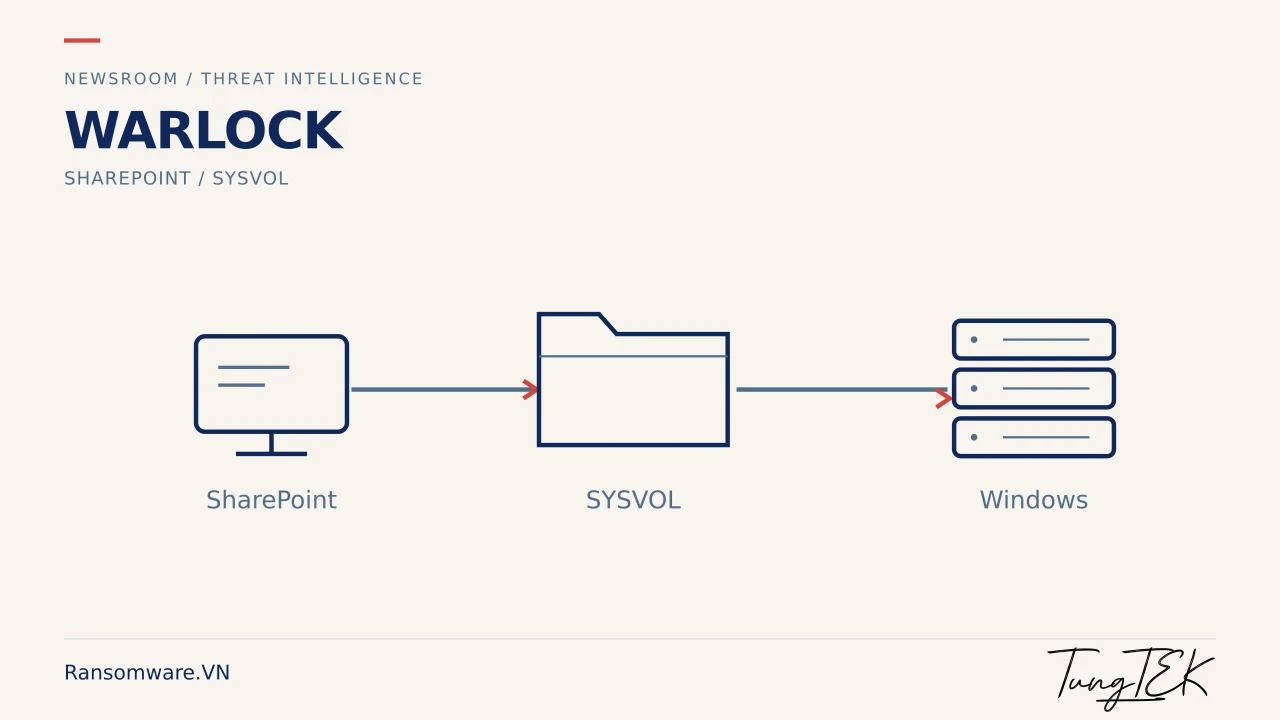
Symantec and Carbon Black's 1 October report highlights SharePoint entry and SYSVOL deployment. A focused reading for enterprise defenders.
AA24-109A is a starting point for technical comparison, not evidence that an individual system is infected with Akira.
Reference analysis of Microsoft's 2024 research, with questions for reviewing access and protecting virtualization infrastructure.
The value lies in explaining what has been confirmed, what remains unknown and what Vietnamese businesses should check next.
A leak-site claim does not mean an incident has been confirmed.
Read our editorial policyHashes, domains, IPs and technical artifacts. Every indicator needs a source, timestamp and context.
View detailsExamine the sequence from initial access to data theft, encryption and disruption.
View detailsCVEs, exposed services and management layers to review in enterprise infrastructure.
View detailsThe education and prevention branch: backups, hardening, checklists, exercises and initial response.
TUNGTEK contributes technical experience and case records approved for publication. Editorial content states its sources and the limitations of the evidence.
A TUNGTEK initiative • Vietnam
About this initiative