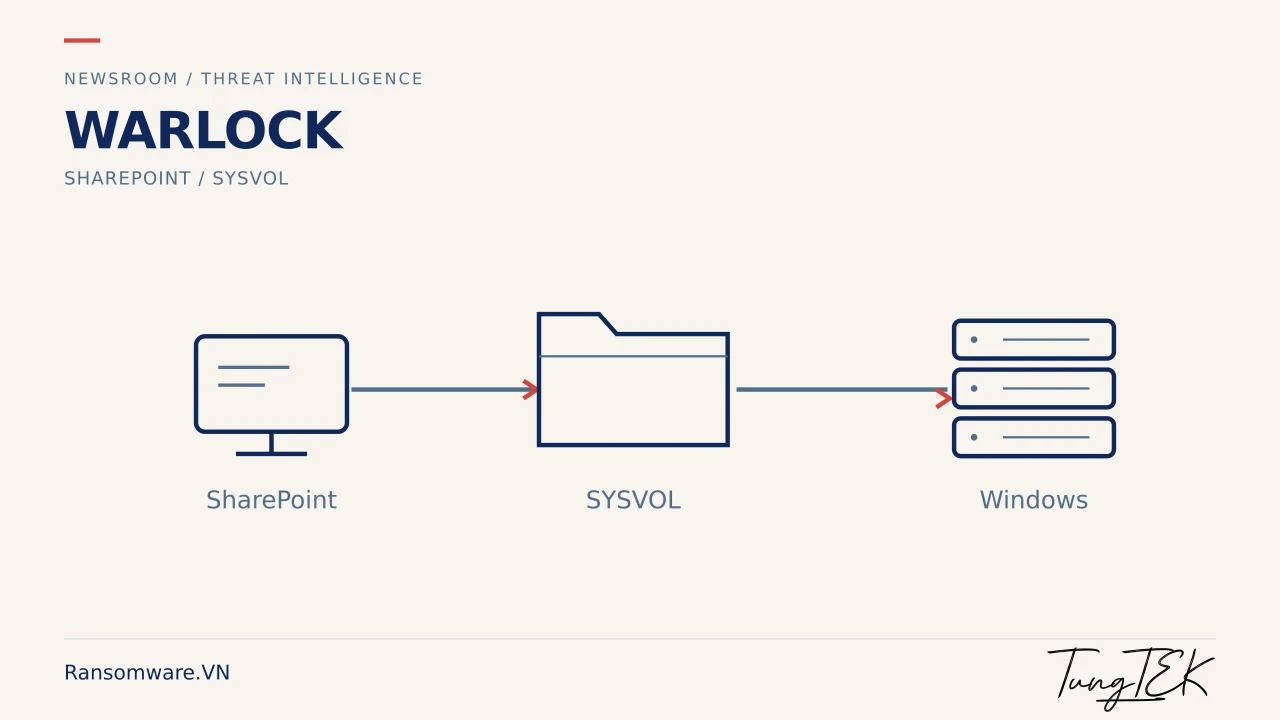
Warlock: use the SharePoint → SYSVOL chain to prioritize investigation
Symantec and Carbon Black's 1 October report highlights SharePoint entry and SYSVOL deployment. A focused reading for enterprise defenders.
Updated: · Vietnam time (UTC+7)
The original report has been checked. Warlock observations and Longlegs/Storm-2603 attribution belong to the research team; Ransomware.VN has not reproduced them or attributed a Vietnam case.
Source published on 1 October 2026. This article explains TTPs; the research sample is not a global or Vietnam statistic.
Observations in the research source
Symantec and Carbon Black report SharePoint exploitation, vulnerable-driver abuse to disable protection, and Warlock staging in SYSVOL. The researchers track the actor as Longlegs, also known as Storm-2603.
Investigative leads need context
An administrative tool or a file in SYSVOL does not establish a Warlock infection. Correlate the actor behind changes, execution origin, privileges and timeline before concluding.
- Compare web-application changes with approved configuration.
- Review SYSVOL writes and permissions alongside execution on destination hosts.
- Correlate driver loading, protection alerts and remote-access sessions.
Limits of use
Keep attribution within the source's scope. Do not infer a case-specific CVE without logs and version evidence, or convert research IOCs straight into a blocking list.
Sources
Each source's scope and date are recorded separately when available. A citation does not independently verify every assessment.
Update history
· Initial publication; event dates, source dates and verification limits are separated.
Corrections policy