Vietnam: checking the StormEncryptor warning and RMM security
A public warning and N-able's notice raise questions about centralized administration. Reference analysis, not a report of a new attack.
Updated: · Vietnam time (UTC+7)
Both public sources have been checked. Publication of the warning and patch notice is verified; the StormEncryptor sample and a Vietnam victim have not been independently verified.
The Vietnam source is dated 29 August 2026; the vendor source is dated 6 August. This reference warning was reviewed on 10 October and must not be presented as a new incident today.
Two sources, two scopes
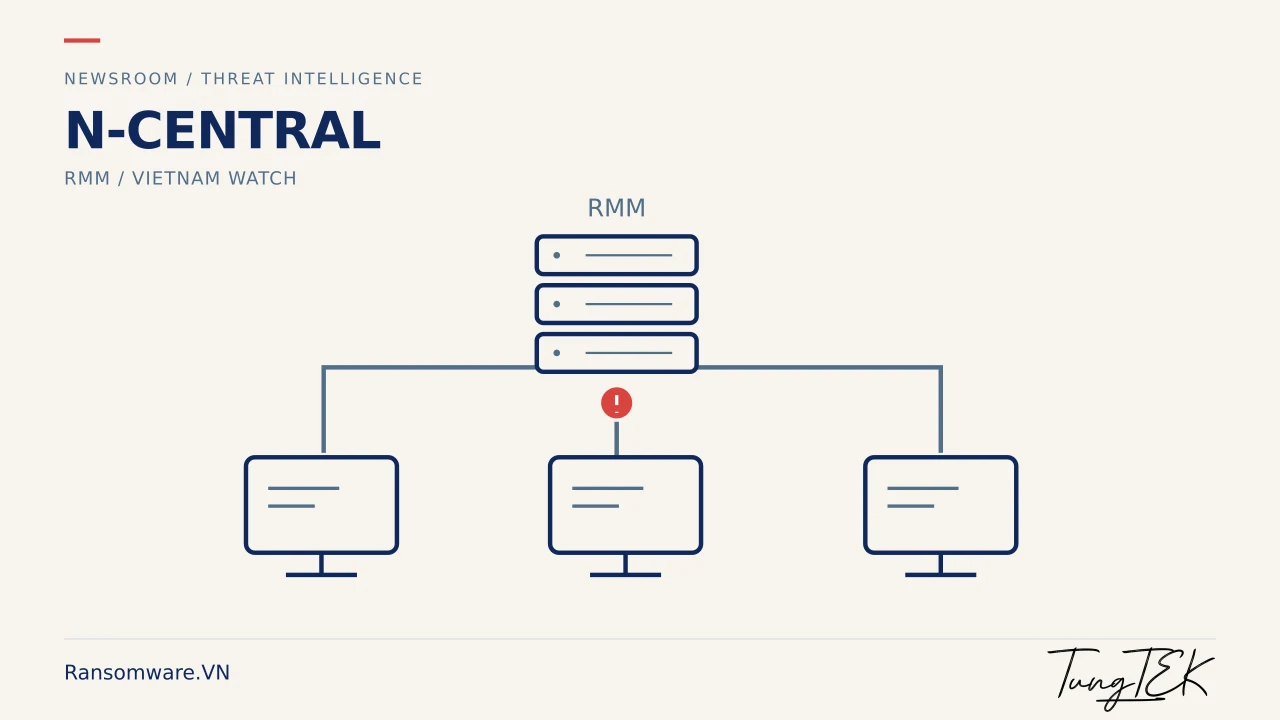
Vietnam's Government News published Hanoi police's warning on 29 August, mentioning StormEncryptor and N-central. N-able's 6 August notice says Hotfix 2 adds mitigations for CVE-2026-18577 and supersedes Hotfix 1.
Checking those documents is not malware analysis or evidence of a specific company's compromise.
Editorial assessment: control the RMM boundary
A management tool able to deploy across many devices needs matching protection boundaries. Review who can issue commands, what changes are approved and which logs remain available.
- Inventory RMM servers, versions and administrative access paths.
- Check current vendor guidance; the August hotfix is not a statement about today's latest version.
- Review accounts, MFA, active sessions and software-deployment history.
- Test recovery from a backup independent of RMM administrative permissions.
What remains unavailable?
The sources used here do not provide victim samples, original logs or a timeline sufficient for Ransomware.VN's own investigation. This warning does not establish incident counts or case-specific attribution.
Sources
Each source's scope and date are recorded separately when available. A citation does not independently verify every assessment.
Update history
· Initial publication; event dates, source dates and verification limits are separated.
Corrections policy