3AM encrypts about 37 machines in UK school estate; AI role remains uncertain
Bitdefender observed a 3AM affiliate extend access through Active Directory trusts. Evidence of AI-generated commands does not establish an autonomous attack.
Updated: · Vietnam time (UTC+7)
Bitdefender's 3 November 2026 original investigation was reviewed. Encryption and attribution to a 3AM affiliate are the investigators' findings; Ransomware.VN has not examined original logs or independently established the victim's identity, initial access, AI model or impact in Vietnam.
The incident occurred in September 2026; 3 November is the report date, not the attack date. Do not link this incident to Bristol or another school breach merely because they share a sector and country.
Evidence: an origin outside endpoint visibility
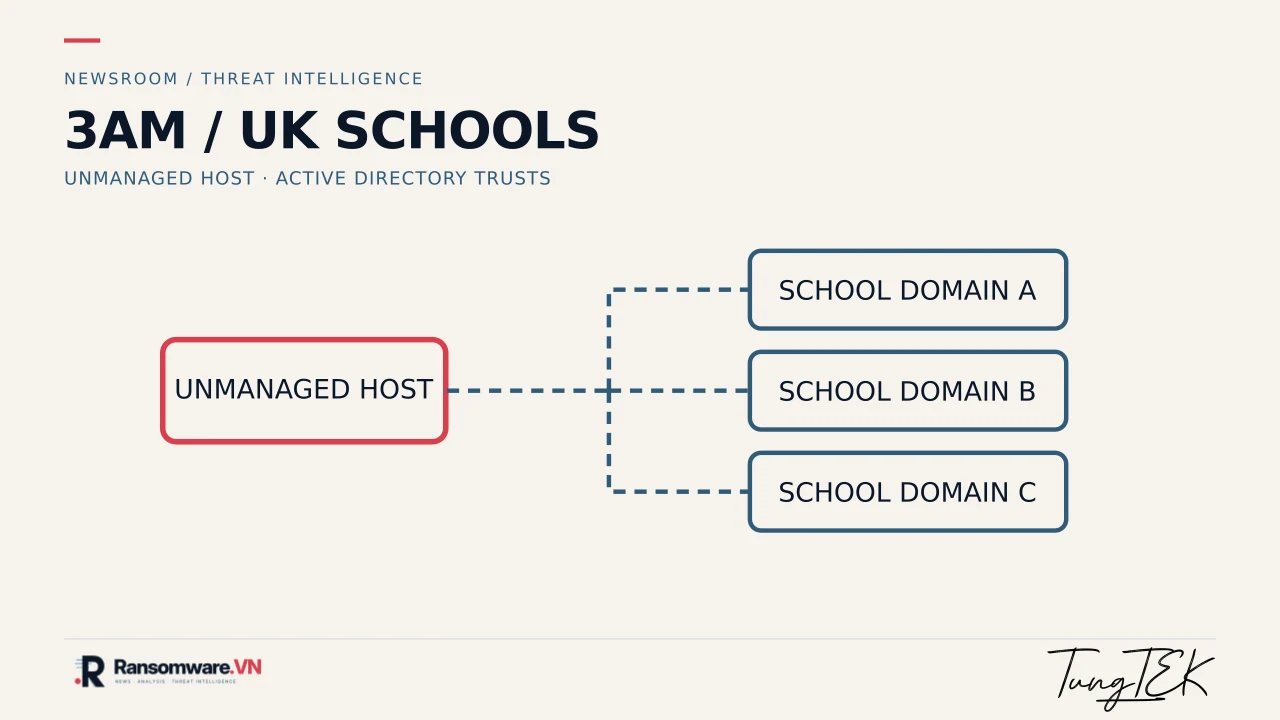
Bitdefender attributed the incident in an unnamed UK school estate to a 3AM affiliate. It observed access to credentials from backup infrastructure, privileged account creation and two-way trusts linking three Active Directory domains. [S1]
The investigators say about 50 machines were reached from a host without their endpoint agent and about 37 were encrypted on the morning of 19 September. These are machine counts from one incident, not counts of schools or campaign-wide victims. [S1]
Evidence of AI assistance does not establish autonomy
Bitdefender says some command contents strongly support language-model assistance. Regular retries are consistent with automation, but a human relaying output between a chat window and the shell could produce the same pattern. The host that might have contained automation was outside its visibility. The model, control mechanism and extent of human involvement remain unknown. [S1]
What defenders can check across domains
- Reconcile new two-way trusts with approved changes; inspect administrator-group changes and new accounts resembling routine service accounts.
- Review access to backup credential stores and alerts for deleted system-state backups; test recovery using a copy outside domain-administrator control.
- Inventory systems without endpoint monitoring that can reach management servers. Correlate network, identity and endpoint logs before drawing conclusions about initial access.
Sources
Each source's scope and date are recorded separately when available. A citation does not independently verify every assessment.
Update history
· Initial publication from Bitdefender's original investigation, separating documented encryption from the autonomous-AI hypothesis.
Corrections policy