AhsayCBS: earlier patches incomplete; review backup servers
Research published on 15 October adds evidence of AhsayCBS exploitation. Check replacement hotfixes and compromise traces; ransomware was not observed in the described cases.
Updated: · Vietnam time (UTC+7)
Cross-checked Ahsay, Bitdefender, Huntress and NVD publications. Ransomware.VN has not independently investigated the systems or malware samples and has not confirmed any Vietnam victim.
Published on 16 October 2026, based on new research dated 15 October and the vendor hotfix notice dated 12 October. This is a backup-infrastructure advisory, not confirmation of a ransomware campaign.
Evidence: new research dated 15 October
Bitdefender MDR reported observing exploitation of the AhsayCBS chain. It observed no encryption, data exfiltration or ransomware deployment in the described cases. The activity is not assigned to a ransomware family.
Evidence: check the complete build number
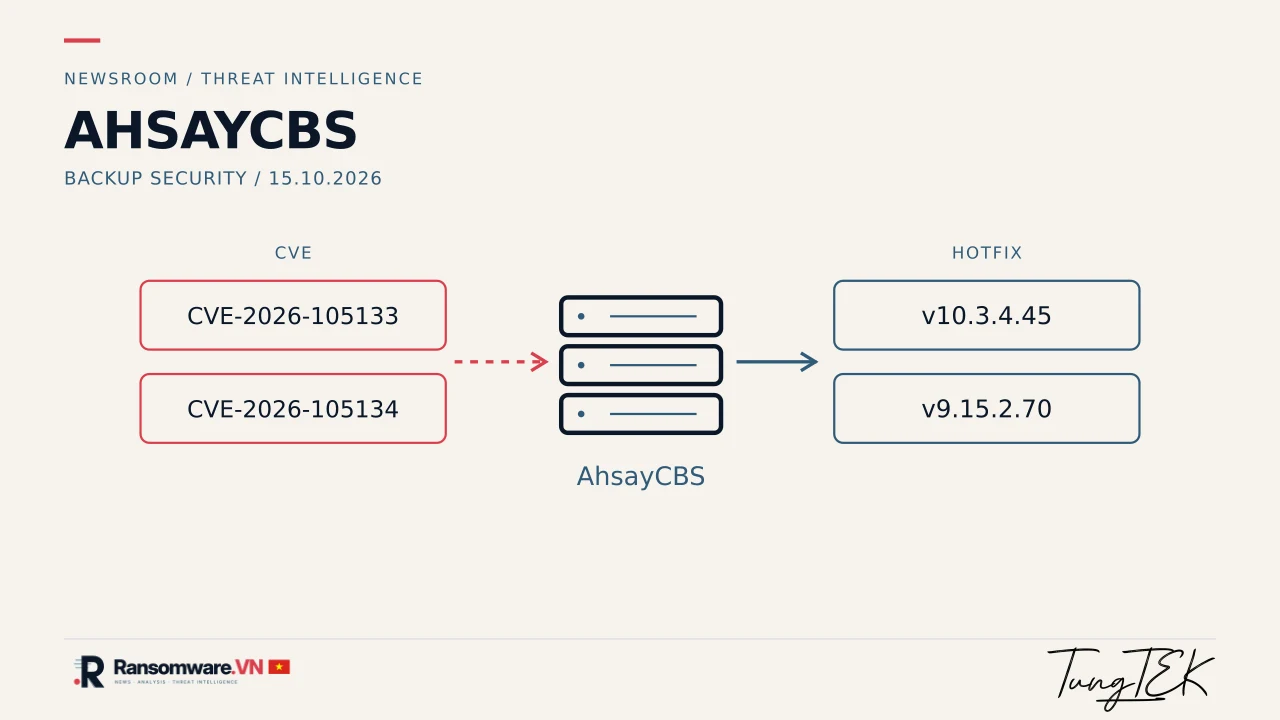
Ahsay's 12 October notice says v10.3.4.0 and v9.15.2.59 were incomplete fixes. It directs v10 users to hotfix v10.3.4.45 and v7, v8 and v9 users to v9.15.2.70, followed by a server reboot. Huntress also verified hotfix v10.3.4.45 against this entry point.
Evidence: read CVEs alongside the newer notice
NVD classifies CVE-2026-105133 as improper authentication and CVE-2026-105134 as OS command injection. Older NVD wording still lists 10.3.4 as unaffected; version decisions should be checked against Ahsay's newer build-specific guidance.
Technical assessment: protect the recovery path
- Inventory AhsayCBS servers, check complete build numbers and network reachability, and contact your provider if backup is operated as a service.
- Patching and compromise assessment are separate tasks: preserve logs and review webshells, unusual child processes and unauthorized remote-access services. If compromise indicators are found, isolate the host and plan trusted recovery.
- Ransomware.VN recommends restore testing and a separate backup copy. This is a defensive priority, not evidence that backups have been destroyed.
Sources
Each source's scope and date are recorded separately when available. A citation does not independently verify every assessment.
Update history
· Published VI/EN editions, cross-checking 15 October research and 12 October hotfix guidance. Exploitation evidence is separated from ransomware risk; no Vietnam impact confirmed.
Corrections policy