AOMEI Backupper update tampering: why endpoint review still matters
GTIG/Mandiant's 15 October and METAL's 16 October 2026 research explain why distribution-server remediation does not clean endpoints. Ransomware is not established.
Updated: · Vietnam time (UTC+7)
Verified refers to the public research reviewed. The researchers collaborated; Ransomware.VN has not examined original samples or logs. These sources do not establish ransomware deployment or an affected Vietnamese organization.
Research published on 15–16 October 2026 describes April–July activity, not a new incident occurring on 20 October. The 30 July document is background mitigation guidance. Artwork is illustrative, not evidence.
Evidence: publication and activity dates are different
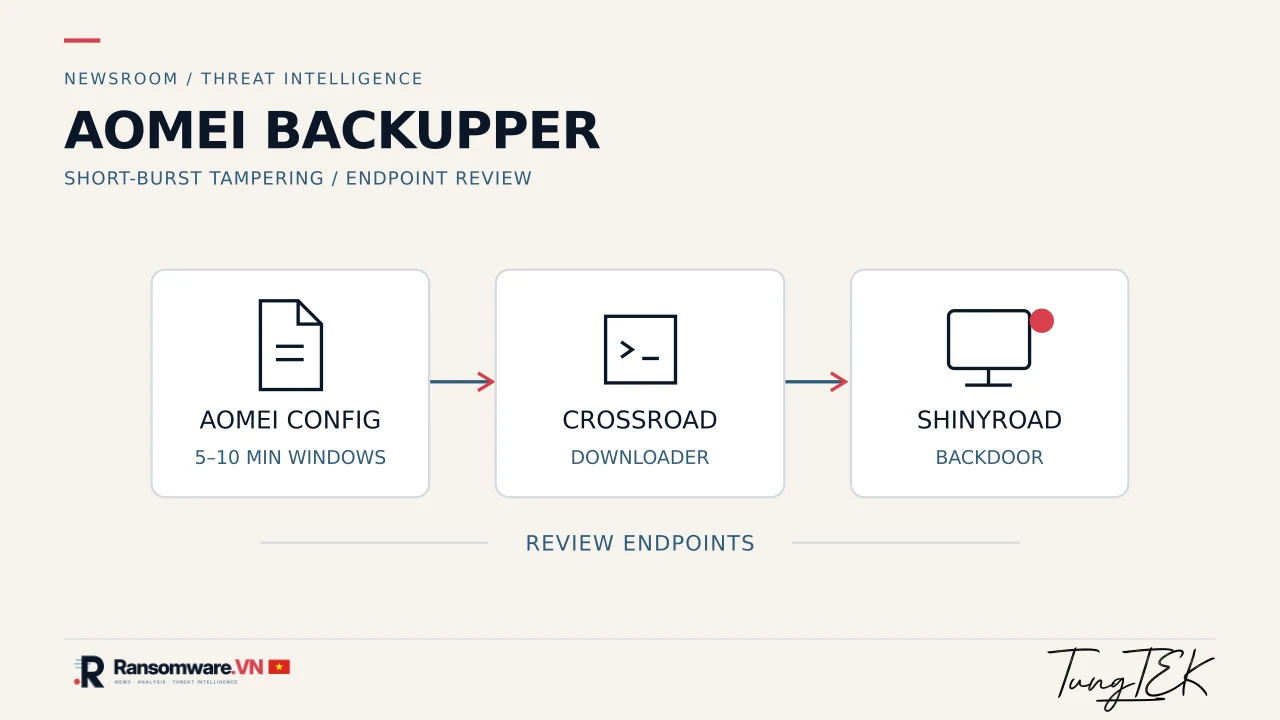
GTIG/Mandiant's 15 October report describes April–July 2026 activity tracked as UNC7017. Distribution configurations were altered for five-to-ten-minute windows, then restored [S1].
Evidence: configuration and checksum share a trust boundary
METAL describes client configurations down_html.ini and Notifycfg.ini lacking cryptographic authentication; the mutable configuration supplies both the URL and checksum [S2]. The researched chain deployed CROSSROAD and the SHINYROAD backdoor [S1, S2], not evidence of a ransomware family.
Evidence: server remediation does not replace endpoint review
AOMEI reported corrective action; METAL had not independently verified containment at publication [S2]. GTIG recommends retrospective endpoint hunting rather than relying on a currently clean URL [S1].
Technical assessment: include backup tools in incident response
Vietnamese IT teams should inventory backup tools and their privileges, preserving logs, cached configurations and process lineage before cleanup. A filename alone does not establish compromise.
GTIG's background guidance recommends software inventory and change control [S3]. Building on that, the newsroom recommends including backup tooling itself in recovery exercises and testing independent copies. This is preventive analysis, not a finding that every AOMEI user or backup was encrypted.
Sources
Each source's scope and date are recorded separately when available. A citation does not independently verify every assessment.
Update history
· Published VI/EN analysis of coordinated 15–16 October research and 30 July background guidance; April–July activity distinguished from publication. Ransomware and Vietnamese impact are not established.
Corrections policy