The Gentlemen names Vietnam Airlines and FPT Software less than 18 hours apart: what is happening?
Two Vietnamese companies are named in DLS records. FPT Software reports no evidence of a related incident. Review of the claims, technical research and anonymized TEKLab lessons.
Updated: · Vietnam time (UTC+7)
DLS records, FPT Software’s official 27 October response and primary technical studies were cross-checked. Not independently verified describes the compromise allegations concerning Vietnam Airlines/FPT Software, not the existence of the listings. Encryption, theft, disruption and a shared campaign remain unverified. Sources reviewed on 28 October 2026, Vietnam time.
Analysis of records from 26–27 October 2026, published at the actual post-review time. AI-assisted editing does not imply personal expert approval. Research observations, defensive interpretation and TEKLab lessons have separate evidentiary scopes. No client data or internal file links are published.
TL;DR — What is actually verified?
Vietnam Airlines and FPT Software were named in The Gentlemen DLS tracking records on 26–27 October 2026, with the two observations less than 18 hours apart. The listings have been cross-checked; the underlying compromise claims have not been independently verified. This article does not confirm harm at either company. FPT Software issued an official response on 27 October, discussed below.
Two observations, less than 18 hours apart
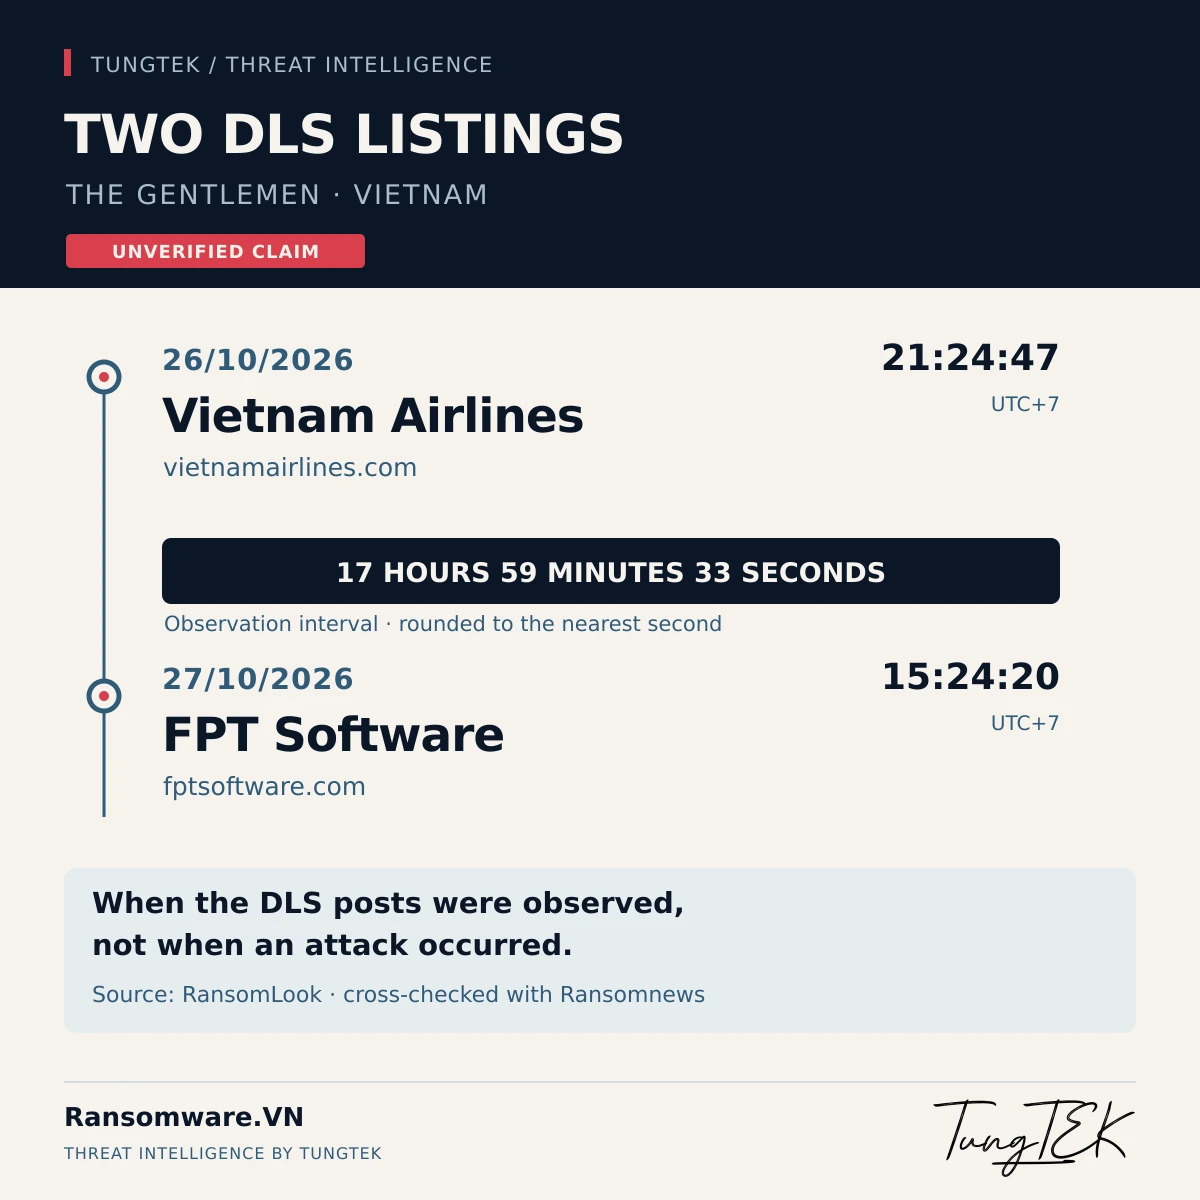
The notable development is the appearance of an airline and a technology company under the same ransomware label. RansomLook defines its timestamps as the first observation of a post. Ransomnews lists both names on the corresponding dates.
| Organization | First observed | Claim status |
|---|---|---|
| Vietnam Airlines vietnamairlines.com | 26 October 2026 · 21:24:47 | Claimed · Not independently verified |
| FPT Software fptsoftware.com | 27 October 2026 · 15:24:20 | Claimed · Not independently verified |
The original timestamps are 17 hours, 59 minutes and 32.594 seconds apart, rounded to 17 hours, 59 minutes and 33 seconds. Publication schedules and tracker polling can influence these observations. They do not establish simultaneous attacks, a shared entry point or the same affiliate.
Verified facts and unresolved questions
Confidence belongs to individual statements. Claimed means a party makes an allegation. Corroborated means additional evidence supports a specified part of it. Confirmed requires sufficiently strong evidence, such as an organizational statement covering that exact issue or reliable investigative findings. Two trackers reproducing one DLS post corroborate the listing, not the alleged damage.
| Question | Vietnam Airlines | FPT Software |
|---|---|---|
| Named in tracking records? | Cross-checked | Cross-checked |
| Systems encrypted? | Unverified | Unverified |
| What data was taken, and how much? | Unverified | Unverified |
| Operational or customer impact? | Unverified | FPT reports normal operations; see its response below. |
| One coordinated campaign? | Insufficient evidence to conclude | |
Reviewed on 28 October 2026: FPT Software has published an official response. No related Vietnam Airlines statement was found within the official-domain search scope; its dynamic press room was not fully exposed to the reading tool. This limitation does not establish that the airline has made no comment.
Corporate descriptions are not proof of stolen data
Vietnam Airlines
The Vietnam Airlines entry on the RansomLook group page mainly contains a corporate description. A domain and public profile do not establish access to an internal network. This review could not authenticate the DLS countdown screenshot mentioned in the input brief and does not use it as evidence.
An extortion countdown can pressure decision-makers into following the attacker's timetable. It does not establish possession of data or guarantee publication when the timer expires. Historical incidents must not be connected to this allegation merely because they concern the same organization.
FPT Software — An official response is available
In its 27 October statement, FPT Software says its investigation found no evidence of a related security incident and operations remain normal. This is the company’s conclusion; Ransomware.VN has not examined its systems.
The next record names FPT Software and fptsoftware.com. Descriptions of business scale or achievements supplied by a claimant do not demonstrate intrusion. This article does not reuse DLS workforce or revenue figures and does not infer compromise of source code, customer information or administrative credentials.
A relevant defensive question for technology providers is how access between provider and customer is separated. Check Point's 13 May 2026 research describes a foreign case in which information from one organization enabled access to another. That illustrates a general supply-chain risk; it is not evidence about FPT or its customers.
The Gentlemen: operators, affiliates and software
MITRE ATT&CK G1058, revised on 30 September 2026, associates The Gentlemen with Storm-2697 and GOLD SHERWOOD. It dates the operation to mid-2025 and the affiliate RaaS offering to September 2025. S9051 describes the software separately from the operating group.
In RaaS, developers provide lockers and infrastructure while affiliates conduct intrusions using their own access and tools. A shared DLS label does not identify a particular operator or a universal playbook. Double extortion combines pressure from encrypted data with threats to publish stolen information. Each alleged impact still needs separate evidence.
Sophos, 1 September 2026, examined 15 incidents involving VPN credential abuse, internal movement and interference with protection or backups; some suspected edge-device exploitation remained unconfirmed. Trend Micro, 9 September 2025, described GPO and WinSCP use in a separate campaign whose initial entry remained uncertain.
Administrators can use these studies to prioritize privileged accounts, remote administration, access logs, outbound transfers and backup changes. This is a defensive interpretation of published research, not evidence that those behaviors occurred at either company named in this article.
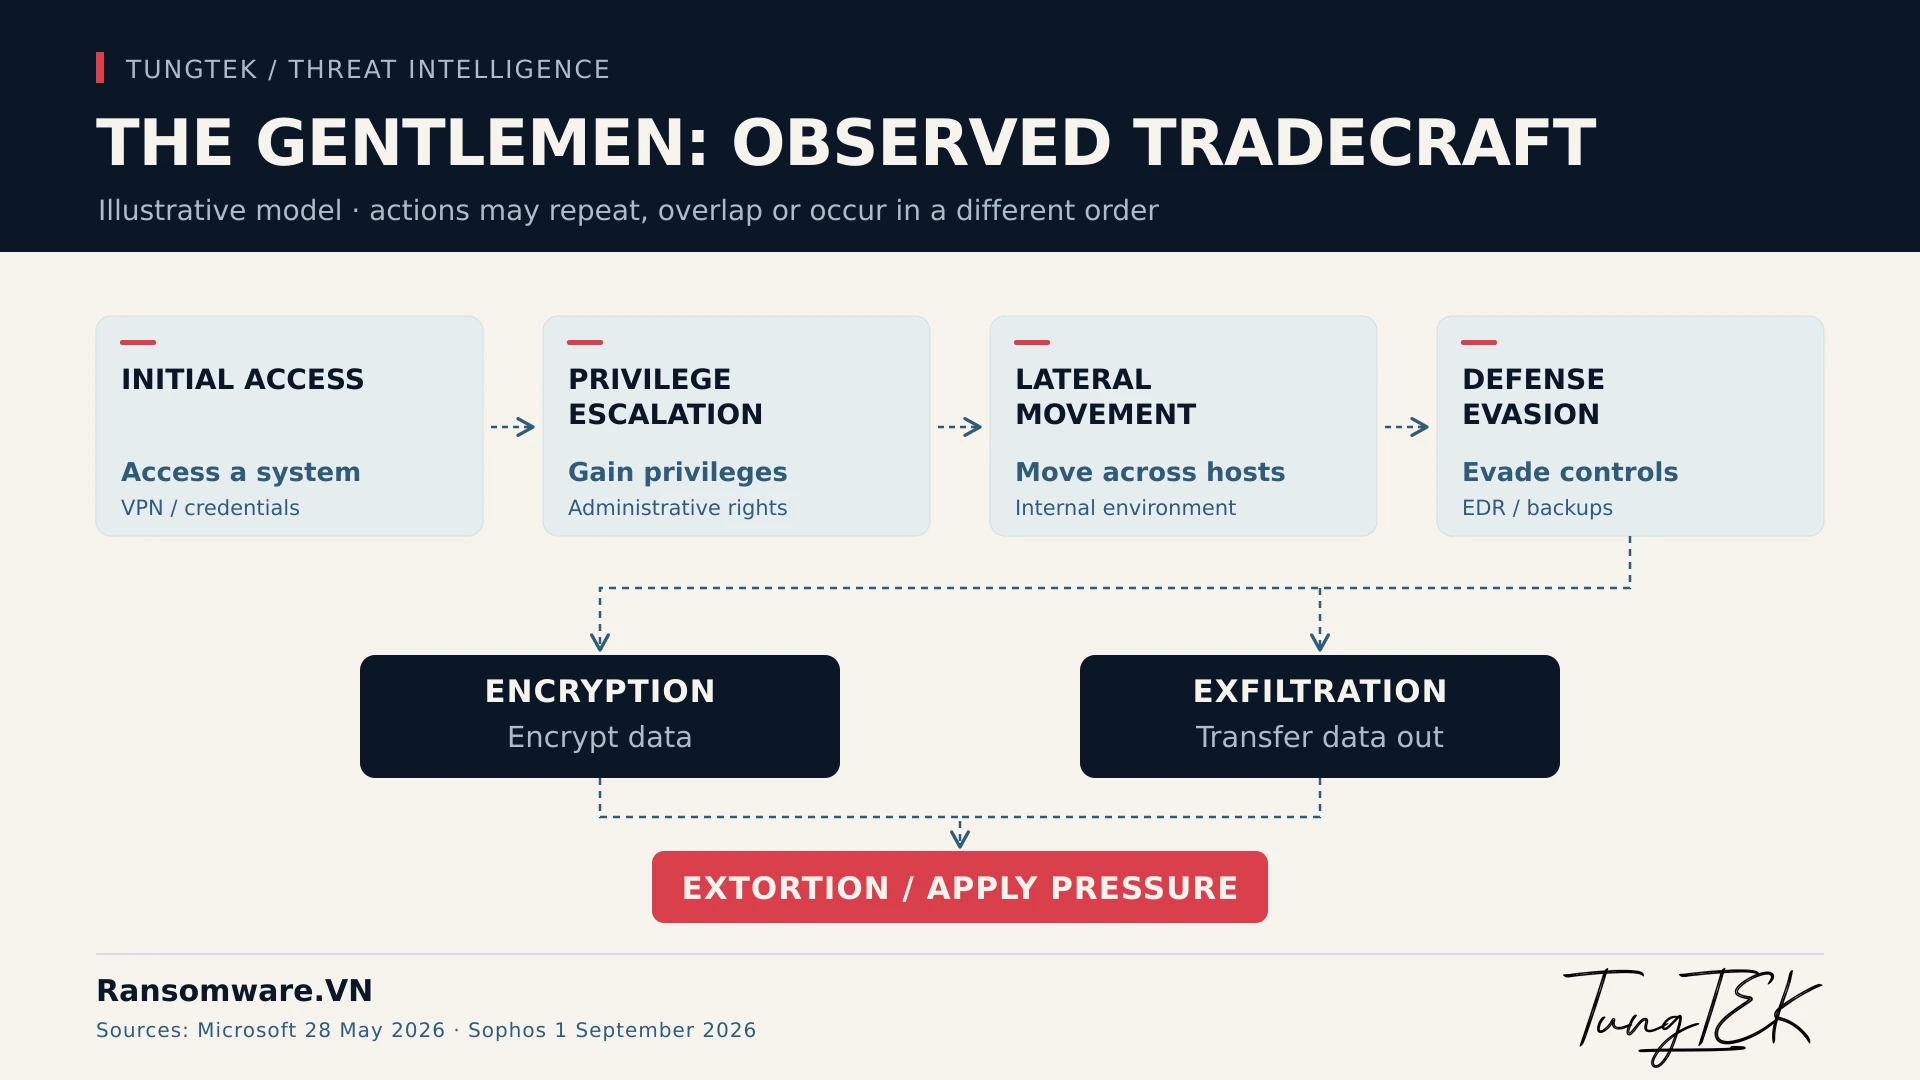
Encryption mechanics and attribution limits
Microsoft's 28 May 2026 analysis describes a Go/Garble Windows sample using XChaCha20, per-file ephemeral Curve25519 keys and partial encryption of large files. Check Point's 20 April 2026 report describes Go lockers for Windows/Linux/NAS/BSD but a C locker for ESXi.
Findings about one Windows sample must not be generalized to every variant. Partial encryption can make a file unusable while leaving some bytes unchanged. For databases and virtual disks, the location of altered regions and surviving references matters more than a raw count of untouched bytes. Fast encryption does not by itself imply weak cryptography or a free decryption route.
Decryption with an appropriate key or tool differs from recovery using backups, replicas or surviving storage structures. Encryption, deletion, overwriting and theft are separate problems that can coexist. Restoring readable files does not undo the consequences of data copied outside the organization.
Sourced investigative leads
The following leads come from public research and have not been confirmed at Vietnam Airlines or FPT Software. They include artifact names and behaviors. Legitimate administration tools are not conclusive indicators by themselves.
| Lead | Source / date | Investigative interpretation |
|---|---|---|
README-GENTLEMEN.txt | Microsoft · 28 May 2026 | Preserve the original, metadata and SHA-256. A filename alone is insufficient. |
Run values GupdateS/GupdateU; tasks UpdateSystem/UpdateUser | MITRE S9051 · revised 30 September 2026 | Correlate executable paths, creating accounts and timestamps. |
| PsExec, WMI, WinRM, SMB and unusual services | Microsoft · 28 May 2026 | Compare with approved administration and destination-host logs. |
| Defender/shadow-copy interference; backup stops and log clearing | Sophos · 1 September 2026; Microsoft | Join endpoint, identity, network and backup evidence. |
| ESXi startup changes, VM termination and datastore artifacts | Check Point · 20 April 2026 | Distinguish legitimate maintenance; preserve host logs and virtual disks. |
TEKLab perspective: recovery starts with the actual system state
Two internal situations supplied by TUNGTEK are used only for anonymized lessons. Ticket numbers, client names, IP addresses, accounts, victim identifiers, amounts and negotiation transcripts are withheld. These are not independent case files confirming the two current allegations. TUNGTEK does not imply it is responding for Vietnam Airlines or FPT Software.
Situation A — Publication deadlines as pressure
The internal record contains a ransom note bearing The Gentlemen's name and messages applying publication-deadline pressure. Assertions of exclusive decryption capability or guaranteed recovery are statements by an extortionist, not technical findings. Decisions should follow examination of backups and data rather than the tone of threats.
The practical lesson is to run two controlled workstreams: preserve communications with restricted access while establishing which independent copies remain usable. Check their age, integrity and application behavior in a clean environment. A statement in a conversation does not replace a recovery acceptance record.
Situation B — Preserving an ESXi environment
According to the internal description, the second situation concerns VMware ESXi with signs associated with The Gentlemen. The public discussion extracts handling principles; it does not publish client screenshots or infer attribution from a folder label. This article provides no basis for claiming a working decryptor or a recovery success percentage.
Preserve VMDKs, snapshot-chain components, VM configuration, host logs and datastore information before intervention. Avoid starting VMs, consolidating snapshots or writing new data before assessing the consequences. Create working copies, record SHA-256 where applicable, and document handlers and transfer times. Retain unchanged inputs so tests can be reviewed.
“Identifying the ransomware family is only a starting point. The recovery approach depends on the system's actual state, encryption scope, surviving data structures and evidence preservation. Two systems affected by the same family can have very different recovery prospects.”
— TUNGTEK / TEKLab · English translation
Is Vietnam becoming a target?
Two prominent names appearing close together are a signal to monitor, not a sufficient sample to establish a campaign specifically targeting Vietnam. Trend analysis requires multiple periods, deduplication and separation of corporate location from affected-system location. DLS counts also depend on publishing patterns and tracker visibility.
The Ministry of Public Security warning of 2 October 2026 discusses The Gentlemen and prevention but does not confirm these two cases. Monitor company notices, official updates and technical findings from lawful sources. Do not download suspected stolen datasets to conduct informal verification or redistribute personal information.
Eight response priorities
- Contain deliberately. Identify suspect hosts and connections with operational owners. Avoid indiscriminate actions that destroy evidence or cause unnecessary disruption.
- Preserve evidence. Retain original notes, logs, encrypted samples and available clean counterparts. Record time zones, collection origin, handlers and SHA-256; restrict access.
- Review identities. From a safe device, inspect privileged accounts, VPN, MFA, sessions, authorized applications and administrative-group changes.
- Check storage management. Review ESXi, NAS, file shares and backup repositories for shared privileges or unmonitored access paths.
- Hunt behavior. Correlate processes, identities and connections in EDR/SIEM. A clean hash result or absence from an IOC list does not exclude intrusion.
- Assess copies. Review snapshots, offline and immutable backups. Establish which predate the incident and who can modify or delete them.
- Test on copies. Separate the recovery environment and validate file structures, databases and applications. Do not test decryptors on original data.
- Coordinate reporting. Assign technical, legal and management contacts and assess applicable incident and personal-data obligations. See the police/PA05 reporting and evidence-preservation guide.
Management needs a status record with accountable owners: what has been checked, what remains unchecked, what evidence exists and which decisions are pending. Separate service-restoration goals from investigation goals while coordinating both workstreams. Time pressure must not turn an investigative hypothesis into a public conclusion.
TUNGTEK | Ransomware Recovery & Digital Forensics
TUNGTEK assesses recovery options for Windows Server, VMware ESXi, NAS, SQL Server and enterprise storage using each incident's actual condition. RFC — Ransomware Fast Check — examines notes, sample files, logs, backups and surviving structures to propose extraction, recovery or decryption where supported by evidence, while protecting client confidentiality.
For encrypted-data incidents, contact TUNGTEK for technical assessment and an appropriate response approach: CuuDuLieuMaHoa.com · 0963509115. This service note does not establish a relationship with either named company.
Sources
Each source's scope and date are recorded separately when available. A citation does not independently verify every assessment.
Update history
· Published the combined VI/EN analysis after checking DLS timestamps, technical research and FPT Software’s 27 October response. The compromise allegations remain unverified.
Corrections policy