Vanderbilt restores some services; full recovery may take weeks
The 10 November update allows device use and restores Wi-Fi plus selected applications. Data-access scope and BYOD’s claims remain unconfirmed.
Updated: · Vietnam time (UTC+7)
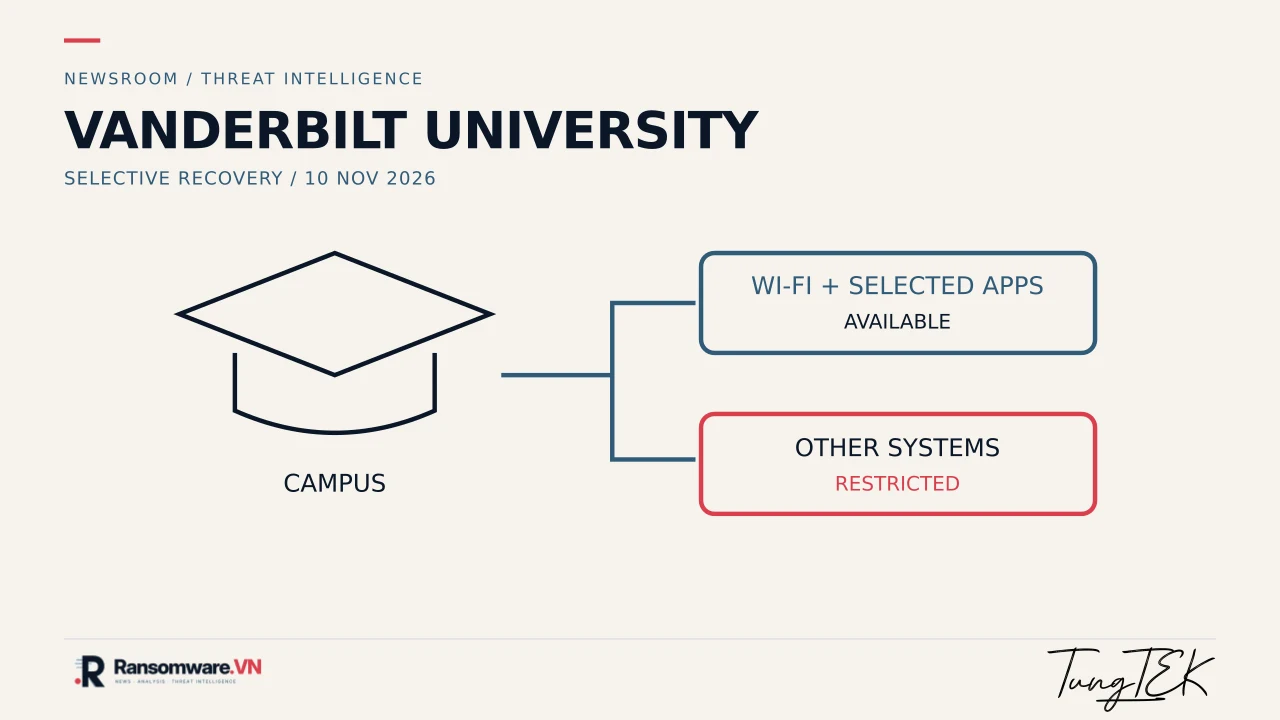
Reviewed the official 10 November 6 p.m. Nashville update. Devices and selected services may be used while possible data access remains under investigation. The university has not confirmed ransomware, encryption, data theft or BYOD involvement.
Original publication date: 10 November. The university’s 10 November 6 p.m. Nashville update permits device use, superseding the earlier shutdown instruction; it does not establish full recovery.
What Vanderbilt confirmed
In its 10:45 a.m. update on 9 November, Vanderbilt University said its IT team was investigating and containing an incident that might affect devices, systems and cloud services. It asked its community to shut down university devices and disconnect from university Wi-Fi. [S1]
For suspicious file or permission changes, unfamiliar alerts or unexpected authentication requests, the university told users not to troubleshoot on their own and to contact the IT Service Desk from another device or by phone. Its 1 p.m. update said classes were proceeding as scheduled; that does not establish system recovery. [S1]
BYOD’s claim is not an investigative finding
BleepingComputer reported that BYOD claimed responsibility on a leak site and alleged database encryption and data theft. Vanderbilt did not confirm those allegations in the official notice reviewed. [S1][S2]
Initial access, actual encryption, any data copied and incident scope remain unresolved. The same claimed group name is not enough to link this incident to UNM Health. [S1][S2]
10 November update: devices permitted, other systems restricted
The 10 November 6 p.m. Nashville update permits device use; Wi-Fi, Okta/MFA, Outlook, CampusPrint, Brightspace, Zoom and YES are available. Other systems remain restricted. Possible data access is still under investigation, and full restoration may take weeks. [S1]
Sources
Each source's scope and date are recorded separately when available. A citation does not independently verify every assessment.
Update history
· Published VI/EN coverage separating Vanderbilt’s confirmation from BYOD’s unverified claims.
· Added the official 10 November 6 p.m. Nashville update: device use permitted and selected services restored; full recovery may take weeks. Replaced six artwork variants, preserving the original publication date, URL and history. BYOD and data scope remain unconfirmed.
Corrections policy